Connect with us


Microsoft today released a defense-in-depth update for Microsoft Office that prevents exploitation of a remote code execution (RCE) vulnerability tracked as CVE-2023-36884 that threat actors have...

Microsoft’s Visual Studio Code (VS Code) code editor and development environment contains a flaw that allows malicious extensions to retrieve authentication tokens stored in Windows, Linux,...


SAP has released patches for 16 vulnerabilities with Critical, High, Medium, and Low severities. The CVSS scores for these vulnerabilities are between 3.7 (Low) to 9.8...


The top 5 security vulnerabilities for 2023 have been revealed by a recent study, with Apache and OpenSSH services being the most vulnerable. MOVEit and Barracuda Networks’ attacks...


Phantom Speculation and Training in Transient Execution are two novel techniques that have been identified to leak arbitrary information from all modern CPUs. A new technique...


Average response time accelerated from 29 to 19 days, from 2021 to 2022, with lessons from Log4j and other high-profile vulnerabilities having a significant impact on urgency levels,...

The constant deep-learning advancements, widespread microphones, and online services are actively escalating the threat of acoustic side-channel attacks on keyboards. An innovative deep learning model uses a nearby...


The software supply chain encompasses the entire lifecycle of a software product, from its conception and development to its distribution and deployment. It involves a complex...


Horizon3.ai researchers have published some details (but no PoC for now, thankfully!) about CVE-2023-39143, two vulnerabilities in PaperCut application servers that could be exploited by unauthenticated...
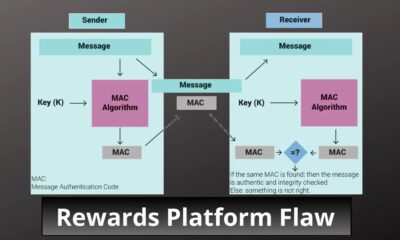

Security vulnerabilities have been reported on points.com between March 2023 and May 2023. On Aug 3, 2023, a group of cybersecurity researchers made these Points.com API vulnerabilities public,...