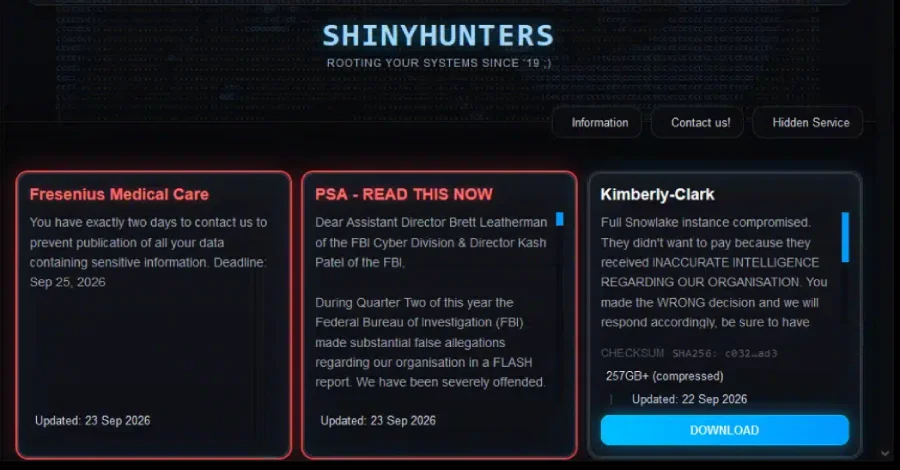
The cyber extortion group known as ShinyHunters has claimed responsibility for a breach of the U.S. Federal Bureau of Investigation, alleging that it obtained sensitive information belonging to FBI employees and people who have applied for jobs at the agency.
The claim emerged Tuesday, but the FBI has not confirmed that its systems were breached or that sensitive personnel data was stolen. The agency said it is investigating reports of unauthorized activity involving its FBI Jobs website.
ShinyHunters Claims Access to FBI Systems
In a statement published on its dark web platform, ShinyHunters claimed it had compromised systems containing information on current and former FBI personnel as well as job applicants.
The group alleged that several FBI services, including systems associated with criminal justice and human resources, were affected. However, no independent evidence confirming the full scope of the alleged intrusion has been publicly disclosed.
Lafayette-based? No — the FBI is a federal agency, and the reported incident is being investigated at the federal level.
FBI Investigating Unauthorized Activity
The FBI acknowledged awareness of claims involving unauthorized activity connected to FBIjobs.gov.
The agency said it was investigating the matter, but did not immediately confirm whether attackers had gained access to internal systems or whether personal information had been exfiltrated.
The distinction is important because claims posted by cybercriminal groups can sometimes exaggerate the scale or impact of an intrusion before investigators establish what actually occurred.
Alleged Oracle PeopleSoft Zero-Day Exploit
ShinyHunters reportedly told The Register that it exploited what it described as a previously unknown Oracle PeopleSoft vulnerability to obtain remote code execution.
The group also claimed it used the alleged vulnerability to access the FBI’s employment website and display a message indicating that the site had been seized.
However, cybersecurity reporting noted that there was no publicly documented PeopleSoft pre-authenticated remote-code-execution zero-day matching the group’s description at the time of the report.
ShinyHunters has previously exploited a different Oracle PeopleSoft vulnerability, CVE-2026-35273, which was used in attacks against enterprise networks earlier in 2026.
Possible Motive Behind the Claimed Attack
ShinyHunters said its alleged operation against the FBI was carried out in response to a May 2026 public service announcement from the agency concerning the group’s activities and attacks involving the Canvas learning management platform.
The group disputed the FBI’s previous characterization of its operations and accused the agency of spreading inaccurate information.
ShinyHunters has also rejected claims that it is part of the decentralized cybercrime collective known as The Com.
Security Experts Urge Caution
Etay Maor, vice president of threat intelligence at Cato Networks, described the alleged FBI breach as an unusually public and provocative claim from a cybercrime group.
He noted that attacks against government and law-enforcement organizations have occurred before, but said a cybercriminal organization publicly claiming to have compromised the FBI represents a particularly notable development.
Maor also pointed to the timestamp attached to ShinyHunters’ post as a potentially useful investigative clue, while emphasizing that such information alone cannot establish where an attack originated.
According to Maor, ShinyHunters has demonstrated an ability to survive arrests, infrastructure seizures and other disruptions by changing its tactics and attracting new participants.
Identity-Based Attacks Remain a Major Concern
Security researchers have increasingly warned that attackers are targeting trusted identities and third-party services rather than relying exclusively on traditional network vulnerabilities.
Recent techniques associated with ShinyHunters have included social engineering against help desks, malicious OAuth applications and stolen authentication tokens linked to software-as-a-service platforms.
These methods can allow attackers to abuse legitimate access mechanisms, making identity security and third-party integrations important components of modern cybersecurity defenses.
Investigation Continues
The FBI’s investigation will ultimately determine whether ShinyHunters’ claims reflect a genuine compromise, how extensive any unauthorized access may have been and whether sensitive information was actually stolen.
Until investigators release additional technical findings, the group’s allegations remain unverified.
Organizations handling sensitive employee and applicant information are likely to continue monitoring the incident closely as authorities work to establish what happened.