Cybersecurity Alerts4 days ago
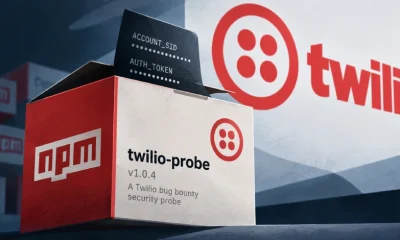
Malicious npm Package Poses as Twilio Bug-Bounty Probe, Can Exfiltrate Credentials
Cybersecurity researchers have uncovered a malicious npm package that pretended to be an authorized Twilio security-testing tool but contained functionality capable of collecting sensitive system information...




Recent Comments