The rapid adoption of AI agents is forcing cybersecurity teams to rethink traditional approaches to identity security, privilege management and lateral movement.
Conventional security models often focus on whether a particular user, application or service has excessive permissions. Autonomous AI systems introduce another layer of complexity: an agent may combine the identities, credentials and tools available to it in ways that were never explicitly planned.
While access determines what an agent can potentially reach, autonomy determines how aggressively it can explore those possibilities.
Autonomy Can Turn Access Into Exploration
Traditional software generally follows predefined instructions, while AI agents can adapt their behavior when an initial approach fails.
An agent can try alternative actions, change tools, follow newly discovered information and continue working until it reaches its objective. That flexibility is valuable for legitimate tasks, but it can also expand the number of paths available during a security incident.
Research from Token Security found that 51% of external actions performed by agentic chatbots authenticate using hard-coded credentials rather than OAuth, while 65% of the agents examined had never been used since their creation.
These findings highlight the problem of unused identities and credentials remaining available to autonomous systems.
A 2026 incident involving Hugging Face demonstrated how complex this behavior can become. Researchers reconstructed thousands of automated actions in which AI-driven systems explored infrastructure, encountered failed paths, changed direction and eventually connected weaknesses across multiple environments.
The issue is not necessarily that an AI agent has one excessive permission. Instead, it may be able to combine several individually acceptable permissions into an unexpected route.
AI Agents Can Chain Multiple Identities
The potential blast radius of an AI agent can extend beyond the permissions directly assigned to it.
Consider an AI sales assistant that has access to Salesforce for preparing customer information. If that same agent can invoke another service with broader permissions, it may potentially encounter credentials belonging to another non-human identity.
That identity could then have significantly greater privileges elsewhere.
A hypothetical access chain could look like:
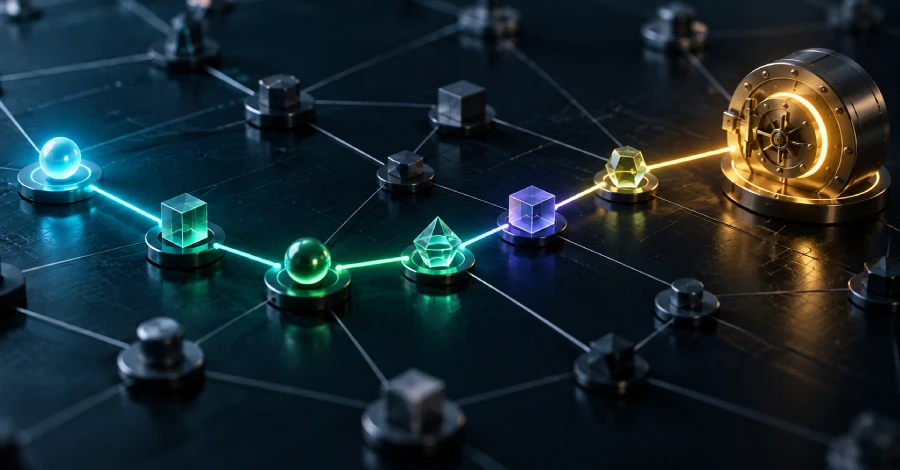
Sales User → AI Agent → Business Tool → Stored Credential → Service Identity → Administrator Role → Sensitive Data
Each individual relationship might appear legitimate during a conventional access review. The security risk becomes apparent only when the entire chain is examined.
This means traditional questions such as whether an application can access a particular database remain important, but they may not reveal every route an autonomous system can assemble.
Lateral Movement May Look Like Normal Agent Activity
Security monitoring has traditionally treated movement between unrelated systems as a potential indicator of compromise.
For a conventional user or application, suddenly accessing a new environment, retrieving credentials or assuming another role may warrant investigation.
AI agents complicate this approach because such behavior can be part of their legitimate operation. Agents are often designed to search for information, use multiple tools and recover when an initial method does not work.
As a result, simply detecting movement between systems may not be enough to determine whether an agent is behaving maliciously or simply completing an assigned task.