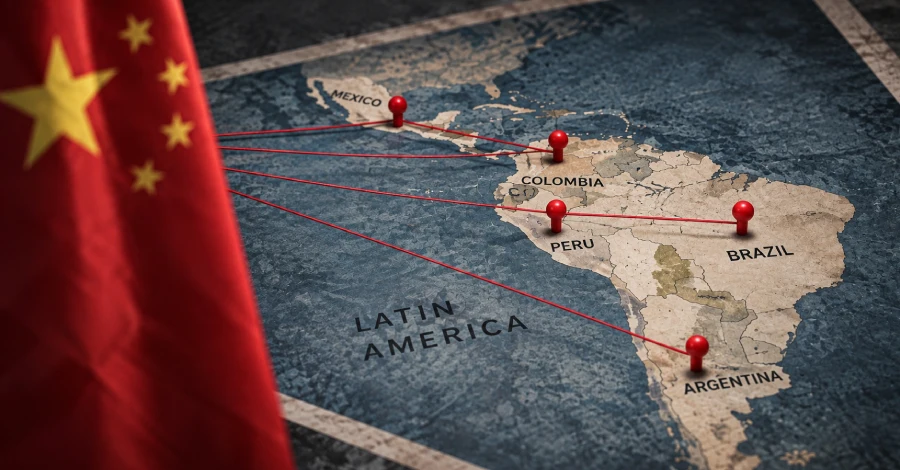
A China-aligned cyber espionage group known as FamousSparrow has been linked to attacks against government organizations across Latin America using a previously undocumented malware implant called SparroWocky.
According to research from cybersecurity company ESET, the activity has been observed since at least August 2025, with most of the group’s recently identified targets located in Latin America.
New C++ Backdoor Replaces SparrowDoor
ESET researchers Alexandre Côté Cyr and Romain Dumont identified SparroWocky as a modular backdoor written in C++. The malware demonstrates advanced knowledge of Windows internals and incorporates several techniques designed to make analysis and detection more difficult.
The name SparroWocky comes from early samples that contained the opening stanza of Jabberwocky, the well-known poem by English writer Lewis Carroll.
The discovery also indicates a shift in FamousSparrow’s malware arsenal. According to ESET, the group appears to have moved from its previously associated SparrowDoor backdoor to SparroWocky as a primary implant.
Extensive Remote-Control Capabilities
Once deployed on a compromised Windows system, SparroWocky can perform a range of surveillance and remote-access operations.
Its capabilities include:
- Executing commands and arbitrary files
- Acting as a TCP proxy
- Collecting information about the infected computer
- Gathering IP addresses associated with network interfaces
- Exfiltrating files from compromised systems
- Capturing screenshots at intervals
- Performing file-management operations
- Removing itself from an infected machine
These functions could allow attackers to maintain control over compromised systems while collecting information of interest.
Open-Source Tools Integrated Into the Malware
ESET researchers found that FamousSparrow incorporated several publicly available projects into SparroWocky’s architecture.
Among them are Mbed TLS, which is used to establish encrypted TLS communications with the command-and-control server, and MinHook, which helps conceal the starting addresses of newly created threads from security software.
The malware also incorporates a COFF Loader to dynamically load and execute plugins directly in memory. Researchers additionally identified a modified implementation related to SilentMoonwalk, also known as StackMoonwalk, which can spoof call stacks associated with MinHook routines.
According to ESET, this represents a notable evolution in the group’s development approach. While FamousSparrow has previously used open-source offensive tools alongside its own malware, SparroWocky demonstrates that the group can integrate such components directly into a customized backdoor.
DLL Sideloading Remains Part of the Attack Chain
Despite the change in malware family, FamousSparrow continues to rely on techniques previously associated with SparrowDoor.
SparroWocky is delivered through a DLL sideloading sequence. In this process, a legitimate executable loads a malicious DLL, which subsequently decrypts and launches the main malware payload.
The researchers have not determined how the attackers initially gain access to the targeted networks.
Government Targets Spread Across Latin America
ESET observed an apparent increase in FamousSparrow activity against high-profile organizations in Latin America beginning around July 2025.
The newly identified backdoor has been deployed against government entities in:
- Argentina
- Ecuador
- Guatemala
- Honduras
- Panama
- Peru
- Puerto Rico
- Venezuela
ESET’s telemetry indicates that approximately 90% of the group’s identified targets were located in Latin America.
Researchers cautioned that it remains unclear whether this concentration reflects a long-term geographic targeting strategy or a temporary shift influenced by geopolitical developments.
FamousSparrow Continues to Evolve
FamousSparrow has been active since at least 2019 and has previously been associated with malware such as SparrowDoor. ESET has also identified overlaps between the group and threat clusters referred to as Earth Estries and Salt Typhoon.
The emergence of SparroWocky highlights the continued evolution of the group’s tooling. By combining custom malware with established open-source components, the attackers can build sophisticated capabilities while incorporating techniques intended to complicate detection and analysis.
For organizations in targeted sectors, the findings reinforce the importance of monitoring suspicious DLL loading activity, unusual encrypted outbound connections, memory-based execution, and other behaviors associated with advanced cyber-espionage campaigns.