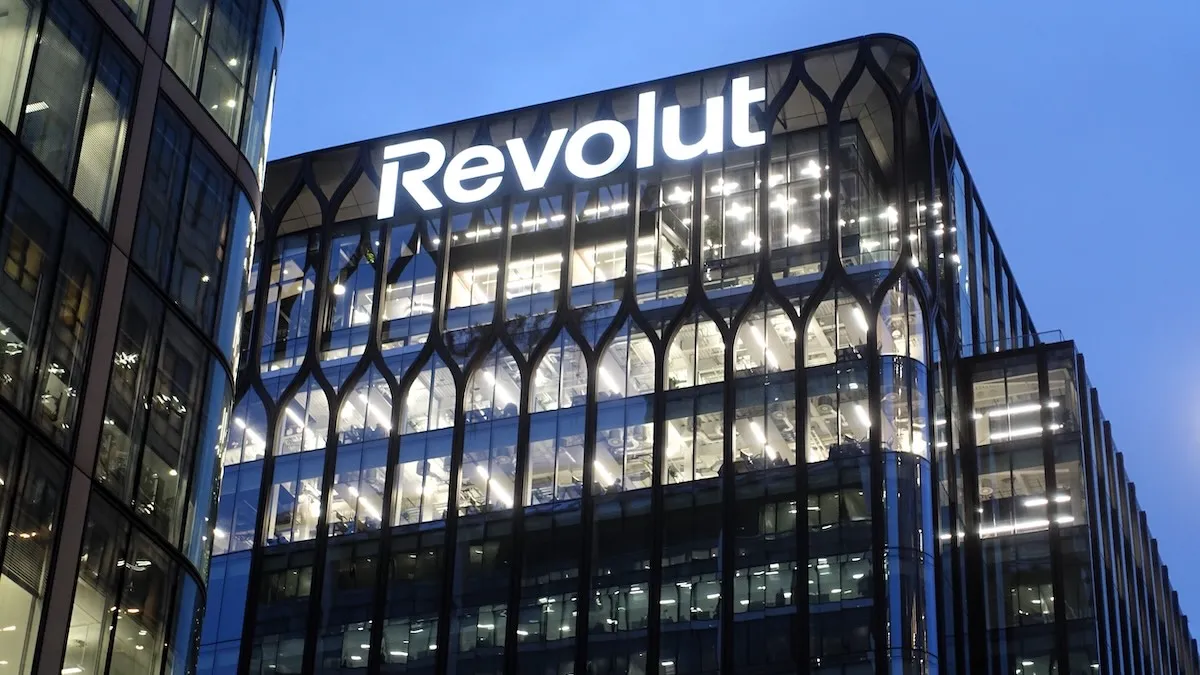
British fintech company Revolut is facing claims that attackers obtained sensitive customer information by impersonating a government agency and submitting fraudulent data requests over several months.
The alleged campaign reportedly exposed personal and financial information belonging to around 680 customers, while a threat actor has publicly demanded $3 million in exchange for not selling the stolen data.
Revolut has said it has not received a direct ransom demand from the individuals or group making the claims.
Hackers Allegedly Exploited Fake Government Requests
Revolut recently notified potentially affected customers that information including personal details, passport information, email addresses, phone numbers and financial data may have been compromised.
According to reports, attackers allegedly obtained the information by posing as an official government authority.
Because financial institutions are required to respond to legitimate law-enforcement requests, the attackers reportedly exploited that process to obtain customer information.
Revolut has not publicly identified the government agency that was allegedly impersonated, nor has it disclosed the total number of affected individuals in response to media inquiries.
Threat Actor Demands $3 Million
A threat actor operating under the name “IAmNotAVillain” publicly claimed responsibility for obtaining Revolut customer information and demanded $3 million.
The actor allegedly threatened to sell the stolen data if the ransom was not paid.
However, Revolut said the company has not received any direct communication or ransom demand from the individual or group behind the claims.
The threat actor also claimed that a sample of the allegedly stolen information had been provided to a former associate who separately claimed involvement in the breach.
Attack Allegedly Continued for Months
According to reporting based on communications with the threat actor, the campaign may have continued for approximately five months.
The alleged operation reportedly began after an attacker obtained access to a government employee’s account through an infostealer infection. The compromised account was then allegedly used to send fraudulent requests to Revolut Bank UAB, Revolut’s Lithuania-based subsidiary.
The attacker claims that the requests were processed without their legitimacy being adequately challenged.
SecurityWeek reported that approximately 680 Revolut customers, described in reports as cryptocurrency holders with substantial assets, may have been affected.
Separate Claims Involve 147GB of Italian Police Data
The alleged attackers have also made separate claims concerning a large volume of information supposedly stolen from an Italian law-enforcement organization.
They claimed that more than 147GB of data was obtained and suggested that the broader campaign lasted six months.
Italian authorities have reportedly opened an investigation into the matter.
The email address allegedly used in the operation appears to be associated with an employee of Italy’s Ministry of the Interior. Cybersecurity firm Hudson Rock said it had identified more than 300 compromised credentials associated with the relevant government email domain.
Infostealer Logs May Have Provided Initial Access
Hudson Rock assessed that the attackers may not have directly infected the government employees whose accounts were subsequently abused.
Instead, the cybersecurity company suggested that the attackers could have obtained previously stolen credentials from infostealer logs.
Infostealers are malware programs designed to collect information such as passwords, browser data, authentication tokens and other credentials from compromised devices. Stolen credentials can later be purchased or reused by other threat actors.
This possibility illustrates how credentials compromised during an earlier malware infection can potentially be repurposed for highly targeted social-engineering campaigns.
Revolut Breach Investigation Continues
The claims surrounding the Revolut incident remain subject to investigation, and some details have been provided by threat actors rather than independently verified.
The incident nevertheless highlights the security risks associated with trusted communication channels and processes used to handle government or law-enforcement requests.
Organizations handling sensitive financial information may need to apply additional verification procedures to high-impact data requests, particularly when attackers can obtain legitimate-looking credentials through infostealer infections or other forms of account compromise.
As investigations continue, affected organizations and authorities are expected to determine the full scope of the compromised information, how the attackers gained access to the relevant accounts and whether additional customers or institutions were affected.