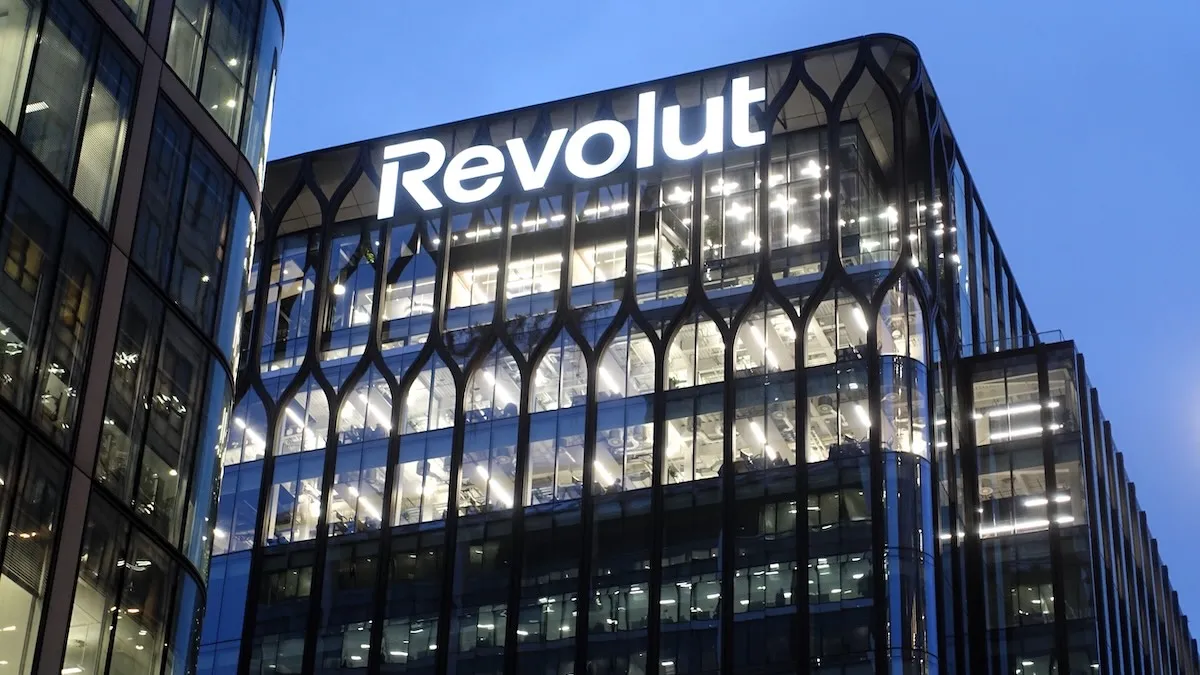
Hackers are reportedly demanding $3 million from financial technology company Revolut after allegedly obtaining customer information through fraudulent government requests over several months.
The incident reportedly involved attackers impersonating a government authority and using compromised official email accounts to submit requests for customer information. Revolut, which is required to respond to legitimate law-enforcement requests, reportedly provided data in response to the fraudulent demands.
The company recently notified potentially affected customers that information including personal details, passport data, email addresses, phone numbers and financial information may have been exposed.
Attackers Allegedly Posed as Government Officials
According to investigations cited in reports, the campaign began after attackers obtained access to a government employee’s accounts through an information-stealing malware infection.
The compromised account was then allegedly used to send fraudulent requests to Revolut Bank UAB, the Lithuania-based subsidiary of Revolut.
The attackers reportedly continued sending requests for several months, with the threat actor claiming that the financial institution did not sufficiently verify whether the demands were genuine.
Revolut has not publicly identified the government organization that was impersonated.
Around 680 Customers Reportedly Affected
Information obtained during the investigation indicates that approximately 680 Revolut customers may have been affected. The individuals were reportedly high-value cryptocurrency users.
The exposed information allegedly included sensitive personal and financial details. Revolut has not publicly confirmed all details surrounding the number of affected customers.
The incident highlights the risks financial institutions face when processing external requests for customer information, particularly when attackers gain access to legitimate government accounts.
Threat Actor Demands $3 Million
A threat actor operating under the name “IAmNotAVillain” publicly demanded $3 million from Revolut on Wednesday.
The attacker allegedly threatened to sell the customer information obtained during the campaign. However, there is currently no indication that the threat actor directly contacted Revolut to formally make the ransom demand.
A Revolut spokesperson told SecurityWeek that the company had not received direct contact or a demand from the individuals or group making the claims.
The threat actor also claimed that a former associate possessed a sample of the allegedly stolen information and had separately claimed involvement in the breach.
Italian Authorities Investigate Separate Data Theft Claims
The attackers have made additional claims involving the alleged theft of more than 147GB of data from an Italian law-enforcement organization.
Italian authorities have reportedly opened an investigation into those claims.
Investigators have also identified a compromised email address associated with the Italian Ministry of the Interior’s government email infrastructure. Cybersecurity researchers reportedly identified hundreds of compromised credentials connected to the relevant domain.
However, claims made by threat actors have not necessarily been independently verified, and the precise scope and origin of the alleged data theft remain under investigation.
Infostealer Malware Suspected in Initial Account Compromise
Cybersecurity researchers have linked the beginning of the campaign to an infostealer infection, a type of malware designed to steal credentials, authentication information and other sensitive data from compromised devices.
Investigators believe the attackers may have obtained access to previously compromised credentials rather than directly infecting every affected government employee themselves.
The suspected use of stolen credentials demonstrates how compromised accounts can potentially be repurposed for convincing social-engineering campaigns against financial institutions.
Investigation Remains Ongoing
The full scope of the Revolut incident remains under investigation. Authorities and cybersecurity researchers are examining how the attackers obtained access to government accounts, how fraudulent requests were processed and what customer information was ultimately obtained.
Revolut has notified potentially affected customers and continues to assess the incident.
The case also highlights a broader cybersecurity challenge for banks and financial technology companies: verifying the authenticity of requests that appear to originate from legitimate government or law-enforcement accounts while protecting customer information from unauthorized disclosure.